The most important quantum deadline is not the day a cryptographically relevant quantum computer arrives. It is the day an adversary decides to steal encrypted data and wait. “Harvest now, decrypt later” attacks are already underway. Motivated actors are exfiltrating information today with no way of decrypting it, in the hope that future quantum capability will unlock it. For banks, the threat is not speculative—it is archival.
Why Long-Lived Data Changes the Calculus
A quantum computer running Shor’s algorithm would break the RSA and elliptic-curve cryptography that secures key exchange, digital signatures, certificates and financial transactions. Expert bodies expect the capability to emerge in the early 2030s, with some placing the threat window in the early to mid-2030s. That sounds distant until you consider data shelf life. Customer identities, loan records, settlement logs, insurance contracts and transaction histories must remain confidential for years, sometimes decades. If that data is stolen today, it may still be sensitive when decryption becomes feasible.
This is why MAS has pushed the industry to act before Q-Day. The central bank has said its aim is for financial institutions to achieve quantum resilience before the end of this decade, and it has signalled progressive timelines for mapping cryptographic assets, prioritising vulnerable systems and building skills and governance. The urgency is not about hardware availability; it is about the exposure that already exists in stored data and long-lived communications.
Visibility Before Migration
The first operational response is cryptographic discovery. Most institutions do not have a complete picture of where cryptography sits across systems, vendors, APIs, mobile clients and legacy platforms. Without that picture, banks cannot know which data flows are most exposed to harvest-now-decrypt-later risk, which algorithms must be retired first, or which third-party dependencies could delay migration.
The second response is crypto-agility: designing systems so algorithms can be swapped without re-engineering the entire stack. Crypto-agility is what allows a bank to move from RSA or elliptic-curve cryptography to NIST-standardised post-quantum algorithms, and later to hybrid or QKD-enhanced models, without restarting the programme each time standards evolve.
A Threat That Crosses Risk Silos
Quantum risk is not only a cybersecurity problem. It intersects with cloud modernisation, API governance, AI deployment, cross-border payment schemes and third-party outsourcing. MAS has emphasised that financial institutions remain wholly accountable for the resilience of services delivered through external parties, regardless of who operates the underlying infrastructure. A bank cannot outsource its quantum-safe migration strategy to a vendor.
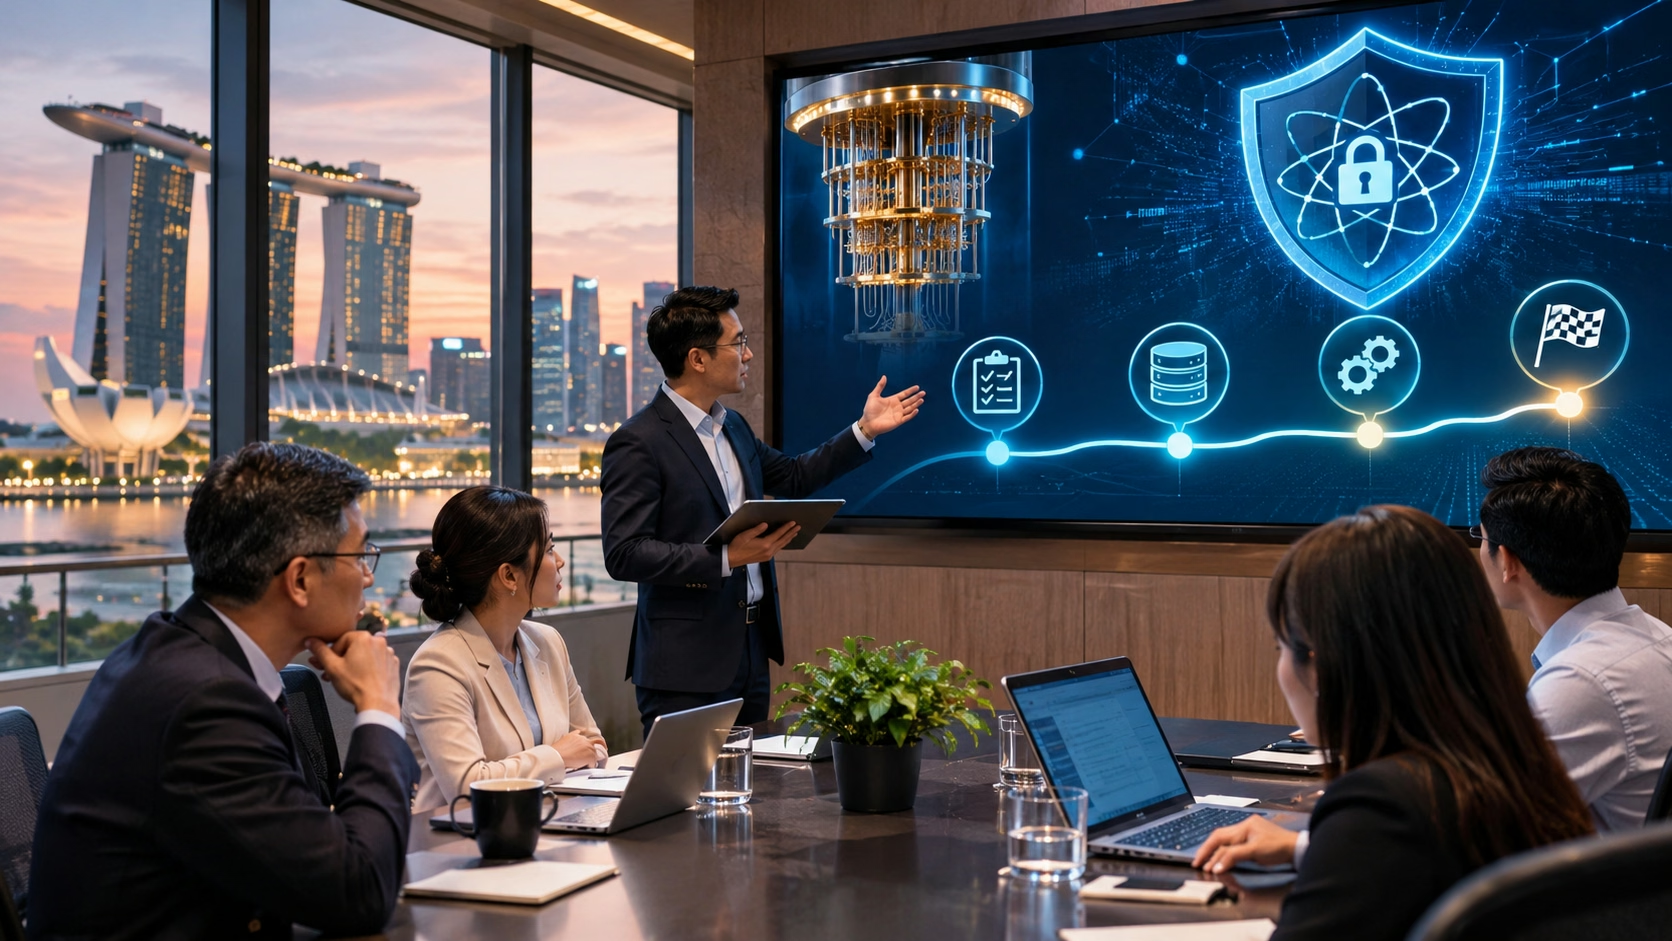
The practical roadmap is unglamorous: inventory, prioritise, pilot, migrate and evidence progress. Singapore’s regulatory stack—MAS consultation timelines, CSA’s migration handbook, the Quantum Readiness Index and the QKD sandbox findings—provides the scaffolding. The remaining work sits inside each institution. CSA’s advisory recommends migration plans by 2027 and completion by 2035, with tighter milestones for critical infrastructure. The data being harvested today will not wait for a comfortable consensus.